XO RBAC Granularity?
-
It doesn't appear that XO provides any granularity when adding users to XO. There are just a User or an Admin? And a User basically can't do anything? Will this be changing with XO6? Will there be RBAC & granularity coming in the future? Some RBAC roles that would be nice to have:
- A Read-Only account for all XO Objects would be nice
- Various Roles, aside from full admin access, like below:
- VM Managment --> user can only manage any VM configs
Ability to create VMs
Ability to remove VMs - Host Management --> ability to add & manage Hosts in XO
- Network Management --> user can only manage Host or VM storage
- Storage Management --> user can only manage Host or VM networking
- Folders --> XO doesn't have these 'objects', but adding ability to create folders in the XO webUI then abiltiy to grant user access to those folders would be great. Would be nice to be able to add VMs to VM folders; or, ability to create Network Folders and assign permissions to manage 'vm networks'; or Storage Folders...again, to grant users ability to add then manage storage for only SRs added to those Folders.
Those are just examples. But, my main reason for this post is to verify I'm not overlooking anything -- there is no role/permissions granularity currently in XO correct? Thanks!
-
I believe what your looking for, is in the Groups and ACL in XOv5 that will give you that. I haven't dug into those settings specifically to say for sure you can or cant do what your asking.
-
@acebmxer Ah, ok...thanks Ace. I'll look at it. At the very least...would probably be best for Vates to revamp this function to make it more intuitive. Appreciate the assist!
-
Well, after a little more digging...I find that this is still not a 'clean' solution imo. I mean, if you're big into APIs....I guess. But, I'd like to see something intuitive in the webUI. Would like to see @julienxovates and @olivierlambert make this a UI feature, instead of a CLI function..or separate URL(swagger) function

Thanks! -
 P poddingue marked this topic as a question
-
If I read the docs right, most of what you're describing exists now, under the name RBAC (it was called ACL v2 while it was being built).
There are eight built-in template roles, including Read only, VMs creator, Network administrator and Storage administrator, which map pretty closely onto your list: https://docs.xen-orchestra.com/users-and-access/rbac#built-in-template-roles.The groups and ACLs @acebmxer mentioned are the older XO 5 system. As you found, the same page says role management currently goes through the REST API, so it's the Swagger page and not buttons in XO 6. Since you're on XO from sources there's no restriction, but for anyone reading this on XOA, the same page says RBAC comes with the Essential+, Pro and Enterprise plans.
A UI for that sounds like a good one for https://feedback.vates.tech/, I don't know whether it's already planned. -
@poddingue
Are you sure that this is implemented (even in sources) yet?
I've been looking forward to this for quite some time. And I still can't find the roles, and functions mentioned in the docs.
Or is it that the UI just isn't developed yet, but the underlying functionality is there. It just needs to be used through the proper API? -
Hi @poddingue ...thank you for the comment. I read the same resources and, though the docs say there are several default roles, sadly, there are not - only 3: Admin, Operator, Viewer.
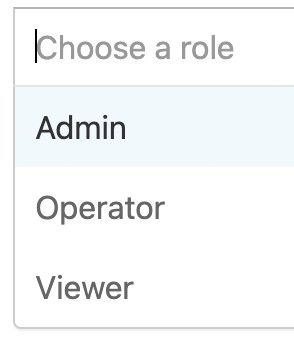
Also, there is no intuitive way to implement said roles even after creating them, which...as mentioned above...isn't too intiutive (imo) to create. Mmm..well, how to implement permissions isn't overly complicated - it's done in the 'ACLs' section. But I'm just used to implementing permissions on various objects within the hypervisor (or central mgmt tool). Maybe it's better doing so only in 1 location. I'll have to think about that one
 But, to @jr-m4 's point...there aren't several default/built-in roles (at least yet) within XO on Sources at least. I'm also looking fwd to this getting develped further. It's sorely needed

-
@coolsport00 Hi !
RBAC/ACLv2 should be on XO6 UI before the end of the year
-
@AtaxyaNetwork Ok, great. Looking forward to it. Thank you!
Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register Login