Subcategories

  • VMs, hosts, pools, networks and all other usual management tasks.

    496 Topics
    4k Posts
    DanpD
    Hi @Tristis-Oris I wasn't able to replicate this issue. My guess is that XO doesn't like something about the file's format. Two areas to check: Open the browser's dev tools window and check for errors in the console Check the xo-server logs for related errors Regards, Dan
  • ACLs, Self-service, Cloud-init, Load balancing...

    107 Topics
    877 Posts
    Bastien NolletB
    Hello @ludalm13, Thanks for your contribution and sorry for not giving an answer earlier. We initially planned to review your PR while doing some additional work on the audit plugin, but our planning evolved and that work was postponed. We'll review your PR in the following days.
  • All XO backup features: full and incremental, replication, mirrors...

    548 Topics
    6k Posts
    S
    @poddingue said: rpm -q sm blktap Both hosts have the following versions installed: sm-3.2.12-25.2.xcpng8.3.x86_64 blktap-3.55.5-12.3.xcpng8.3.x86_64
  • Everything related to Xen Orchestra's REST API

    89 Topics
    656 Posts
    P
    Hi, This was fixed in Latest. But if you need to stay on Stable, you can open a ticket to have a patch.
  • Terraform, Packer or any tool to do IaC

    54 Topics
    507 Posts
    D
    For anyone else who steps through this, I've also installed the latest xen-guest-agent with the below process. Repeat for each host in the environment, 1 at a time from your Helper VM. ### ssh into your helper ### oc debug node/fedora-cmp-1/2/3 chroot /host cd /var/tmp curl -LO https://gitlab.com/xen-project/xen-guest-agent/-/jobs/6041686376/artifacts/raw/RPMS/x86_64/xen-guest-agent-0.4.0-0.fc37.x86_64.rpm sudo rpm-ostree install /var/tmp/xen-guest-agent-0.4.0-0.fc37.x86_64.rpm mkdir /var/tmp/xga && cd /var/tmp/xga rpm2cpio ../xen-guest-agent-0.4.0-0.fc37.x86_64.rpm | cpio -idmv ### From your helper... DRAIN YOUR WORKERS ### oc adm drain fedora-cmp-1/2/3 --ignore-daemonsets --delete-emptydir-data ### log back into fedora-cmp-1/2/3... ### sudo systemctl reboot ### from helper ### oc adm uncordon fedora-cmp-1/2/3 ### login to fedora-cmp-1/2/3 ### chroot /host sudo systemctl enable --now xen-guest-agent And then from XO this is what your VMs will look like. [image: image.jpeg]
  • 1 Votes
    4 Posts
    716 Views
    acebmxerA
    Added local user support. Current sample config file. # Example xo-apply configuration. # Copy this into your own PRIVATE repo, edit, then: # export XO_URL=https://xo.example.lan XO_TOKEN=... # xo-apply diff config.yaml # xo-apply apply config.yaml # # Secrets never go in this file: use ${env:VAR_NAME} placeholders, # resolved from environment variables when the tool runs. # # A section that is ABSENT is unmanaged (xo-apply won't touch or report that # resource type). A present-but-empty section means "manage this type, none # should exist" (only deleted when you pass --prune). remotes: # NFS share on a NAS - name: nas-backups type: nfs host: 192.168.1.50 path: /export/xo-backups # port: 2049 # optional # mountOptions: vers=4 # optional mount(8) options # SMB / Windows share — host is "HOST\share" (single backslash in YAML # double-quoted strings must be written as \\) - name: windows-share type: smb host: "192.168.1.60\\backups" domain: WORKGROUP username: backup password: ${env:SMB_BACKUP_PASSWORD} # path: xo # optional subfolder inside the share # S3-compatible object storage (AWS, MinIO, Backblaze B2, ...) - name: offsite-s3 type: s3 host: s3.us-east-1.amazonaws.com path: my-bucket/xo-backups # bucket/directory accessKey: AKIAEXAMPLE secretKey: ${env:S3_SECRET_KEY} region: us-east-1 # protocol: http # for http-only endpoints (e.g. local MinIO) # Directory local to the XO VM (e.g. a mounted USB disk) - name: local-disk type: local path: /mnt/backup-disk backupJobs: # Delta (incremental) backup of every VM tagged "critical", every night - name: nightly-critical mode: delta vms: tag: critical remotes: [nas-backups, offsite-s3] settings: # optional global job settings, passed through to XO concurrency: 2 # timezone: America/New_York # maxExportRate: 104857600 # bytes/s # nRetriesVmBackupFailures: 2 # reportWhen: failure schedules: - name: nightly cron: "0 2 * * *" retention: 14 # backups kept on the remotes # snapshotRetention: 3 # snapshots kept on the pool # timezone: America/New_York # enabled: false # schedules are enabled by default # Weekly full backup of specific VMs, selected by name - name: weekly-full mode: full compression: zstd vms: names: [dc-01, mail-01] # ...or select by uuid: uuids: [770aa52a-fd42-8faf-f167-8c5c4a237cac] # ...or pass a raw XO smart-mode pattern for anything more complex: # raw: # type: VM # tags: # __or: [[prod]] remotes: [nas-backups] schedules: - name: weekly cron: "0 3 * * 0" retention: 8 # Disaster Recovery / Continuous Replication: instead of (or in addition to) # remotes, target one or more SRs. mode:full => DR, mode:delta => CR. - name: dr-critical mode: full # delta = Continuous Replication vms: tag: critical srs: [4991d4aa-ed84-599b-7d19-97f2f943a366] # target SR UUID(s) # remotes: [] # SR-only is fine; may be combined with remotes schedules: - name: hourly-dr cron: "0 * * * *" retention: 3 # replicas kept on the SR # Metadata backups: pool metadata and/or XO's own configuration. metadataBackups: - name: xo-config xoMetadata: true # back up XO's own config pools: [939ed551-fbd6-9868-52d8-d3997b7bf7da] # pool UUID(s) for pool metadata remotes: [nas-backups] schedules: - name: daily cron: "0 21 * * *" xoRetention: 7 # XO metadata backups kept poolRetention: 7 # pool metadata backups kept # Mirror backups: copy an existing remote's backups onto other remote(s), # e.g. push local backups offsite to S3. mirrorBackups: - name: offsite-mirror mode: full # full or delta, to match the source backups sourceRemote: nas-backups remotes: [offsite-s3] schedules: - name: nightly-mirror cron: "0 5 * * *" retention: 14 # Sequences: run backup schedules one after another. Each step names a job and # one of its schedules (from any job kind above, or already in XO). The sequence # has its own cron for when the whole chain runs. sequences: - name: nightly-then-metadata steps: - { job: nightly-critical, schedule: nightly } - { job: xo-config, schedule: daily } cron: "0 22 * * *" # enabled: false # sequences are enabled by default # timezone: America/New_York # Local users (XO's internal auth provider). Users created by an external auth # plugin (LDAP/SAML/GitHub) are NOT managed here and are never pruned. # # Passwords are write-only: XO never returns them, so a real password can't be # exported or diffed — but XO REQUIRES a password to create a user. So `export` # writes the placeholder `password: ChangeMe` for every user. # ⚠️ CHANGE these before importing into a real XO (or use a ${env:...} ref), # otherwise every new user is created with the password "ChangeMe". # The password is only used when a user is CREATED; for an existing user it is # ignored (change it in the XO UI). Only `permission` is compared for drift. users: - email: ops@example.com password: ChangeMe # required by XO; change before import permission: admin # none | read | write | admin (default: none) # Local groups. Members are referenced by email and resolved to ids at apply # time; each member must be a user defined above or already present in XO. groups: - name: operators users: [ops@example.com]
  • v6 left navigation bar

    2
    3
    0 Votes
    2 Posts
    875 Views
    olivierlambertO
    Thanks, I made the feedback to the XO team, this will be fixed ASAP.
  • Netbox sync and empty virtual disks

    3
    0 Votes
    3 Posts
    860 Views
    B
    @poddingue Thanks for the reply. I have been checking the source code of the Netbox plugin over the weekend and added the necessary code to enable the virtual disk sync. In Netbox itself, you do need to add the correct permission for it to work. Will do some more testing during the week, and create a pull-request once I'm satisfied with the result. Up to the Vates if they want to merge it into the main branch. Thank you for your reply!
  • xo-server executable not found

    3
    0 Votes
    3 Posts
    667 Views
    E
    @poddingue said: usually looks like an update that got interrupted or only half-applied Thinking back on it, I think that may be the issue. in that I was too quick off the mark rebooting after the base upgrades. @poddingue said: I think the gentler recovery before rebuilding would have been re-running the updater from the CLI Kinda tried that, but: [18:47 09] xoa@xoa:~$ xoa check -bash: xoa: command not found [18:47 09] xoa@xoa:~$ sudo xoa-updater --upgrade [sudo] password for xoa: sudo: xoa-updater: command not found [18:48 09] xoa@xoa:~$ But regardless, I'm all good now. Cheers.
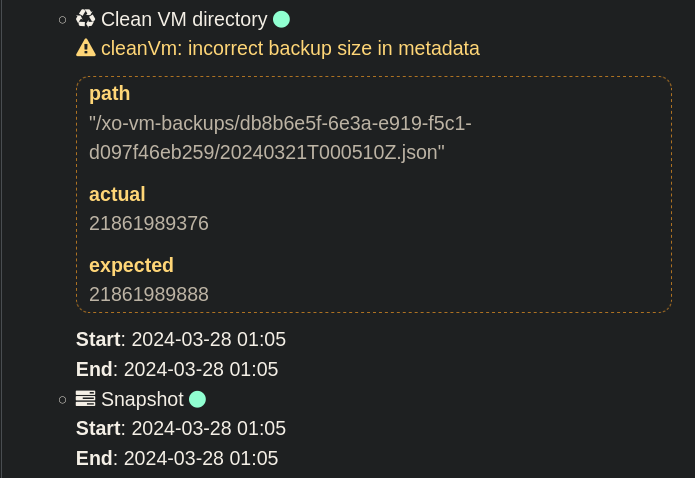
  • cleanVm: incorrect backup size in metadata

    20
    1
    0 Votes
    20 Posts
    7k Views
    M
    @poddingue Not seeing it anymore
  • XO-6 Cannot connect to server over Unifi SD-WAN, XO-5 works well

    4
    0 Votes
    4 Posts
    777 Views
    olivierlambertO
    Maybe you can check for a bigger timeout on your UDM?
  • MTU change

    12
    0 Votes
    12 Posts
    9k Views
    bleaderB
    @Andrew I did suspect that would be sufficient, but we need to think at feature level, and as mentionned there is no such thing we could do "quickly" for linux and other OSes. I anyway did a brain dump of my investigation before posting my previous message and we do now have an entry in the roadmap for it, which was not the case previously.
  • Disaster Recovery Backup - how to restore?

    16
    0 Votes
    16 Posts
    7k Views
    olivierlambertO
    It hurts (4y ) but I'm glad we finally managed to get what you needed!! Thanks for posting a comment in here after all this time [image: 21cd8648-f61e-46d9-a52f-4ec55a7b7c8b-image.jpeg]
  • Some dashboard loading issues with v6

    Solved
    27
    5
    0 Votes
    27 Posts
    6k Views
    acebmxerA
    @simonp said: @acebmxer Hi, Thanks to your help we were able to identify an issue with Redis that we think is the source of the v6 dashboard loading issue. Could you try and checkout the fix_redis_encryption_issue branch, rebuild xo and restart ? This should solve the 401 issues. Switched back to Master branch and made some changes to my install script. add diagnostics for missing XO 6 web UI build artifacts Plain bash [[ -f ]] fails silently on unreadable paths owned by SERVICE_USER, causing false-positive missing-artifact warnings. Switch all file/dir tests and grep calls to use sudo. SUCCESS] Xen Orchestra built successfully [INFO] Build verification passed: dist — all JS chunks present. [INFO] Build verification passed: dist — all JS chunks present. [INFO] Creating systemd service... [SUCCESS] Systemd service created and enabled [INFO] Configuring sudo for xo-service (mount/umount/findmnt)... [SUCCESS] Sudo configured for xo-service (mount, umount, findmnt) [INFO] Applying security hardening... [INFO] Starting xo-server service... [INFO] Waiting for Xen Orchestra to become ready (up to 60s)... [INFO] Not ready yet (attempt 1/10), retrying in 6s... [SUCCESS] Xen Orchestra is ready (HTTPS on port 443) [SUCCESS] Update completed successfully! [INFO] New commit: 0f29421627c7 v6 Dashboard still loading correctly. Thank you for the fix.
  • XOA - Memory Usage

    48
    2
    0 Votes
    48 Posts
    15k Views
    acebmxerA
    @florent said: @acebmxer back to work thank you for yor patience and help on this. I feel that it's not the same issue , with abrupt increase W will try our best to also fix this one Yes i replied to ticket also.... Yes you can do what is needed to XOA. Just looked at memory and it dropped.... [image: Screenshot_20260527_055458.png]
  • XO Console: Modifier keys stuck, unable to enter passwords

    14
    0 Votes
    14 Posts
    4k Views
    poddingueP
    Thanks for the clarification, @dsmteam !
  • Edit a Bond to Remove a NIC?

    2
    0 Votes
    2 Posts
    533 Views
    poddingueP
    Take it with a grain of salt, but I think bonds are usually managed as a whole rather than edited port by port in the UI. As far as I can tell, the supported route is from the network section in Xen Orchestra (the bonding part of the infrastructure docs is here: https://docs.xen-orchestra.com/xo5/manage_infrastructure#network-bonding), and on the CLI side, the bond commands are documented at https://docs.xcp-ng.org/appendix/cli_reference#bond-create (there's a matching bond-destroy command alongside it). My honest guess is you may end up destroying and recreating the bond with the four ports you want to keep, since I'm not sure removing a single member in place is exposed anywhere, but I could easily be wrong. If there's a cleaner way that avoids the recreate, someone will let us know.
  • Xen Orchestra has stopped updating commits

    34
    0 Votes
    34 Posts
    16k Views
    florentF
    @ducatijosh did you do a yarn build ?
  • 0 Votes
    4 Posts
    853 Views
    K
    Ok I think I have resolved the issue. It appears that if you do not activate either a paid license or the trial, it fails with the import because many of the features are not active until you enable the license and then update the XOA appliance. Once I activated the trial and then updated the appliance again, I was able to successfully import the backup. My hesitation with activating the license before importing the config as the licenses are bound and I didn't want to have to redo the setup if the config did not import. Again, it looks like I need to activate the license first and then I can import the config.
  • Default console username and password on XOA Appliance

    Solved
    12
    0 Votes
    12 Posts
    34k Views
    olivierlambertO
    Hi, See https://docs.xen-orchestra.com/troubleshooting#recover-web-login-password
  • Building from source, now introduces local changes in typed-router.d.ts?

    Solved
    11
    0 Votes
    11 Posts
    2k Views
    J
    @MathieuRA I noticed you merged https://github.com/vatesfr/xen-orchestra/pull/9787 I just tried it. And it does seem to fix my original issue! Thank you! I am always impressed by you guys. Making testing and reporting upstream (to you guys) a good experience!
  • load-balancer : Affinity to Host groups

    6
    0 Votes
    6 Posts
    1k Views
    Mitchel-APDM
    @olivierlambert In my understanding, Anti affinity tags only looks for the tags that are attached to the VM. For example: Datacenter 1 Host 1 VM1-1 Host 2 VM1-2 Datacenter 2 Host 3 VM2-1 Host 4 VM2-2 VM1-1 and VM1-2 should be able to migrate to Host 1 and Host 2. VM2-1 and VM2-2 should be able to migrate to Host 3 and Host 4. But VM1-1 and VM1-2 should never be able to migrate to Host 3 and Host 4. VM2-1 and VM2-2 should never be able to migrate to Host 1 and Host 2. With the current (Anti) Affinity tags, it will only look to the tags attached to the VM, so in the example it would be possible for VM1-1 to go to Host 4, if VM2-2 would be at Host 3 together with VM2-1. But if we could tag the hosts, it would not be possible for VM1-1 and VM1-2 to be on Host 3 and Host 4
  • Lost connection to ISO Repository

    10
    2
    0 Votes
    10 Posts
    2k Views
    A
    @Pilow Apologies for the late reply. Thank you for sharing the work around. I have tried it and confirmed that the work around works. I hope they can find a solution for this issue.
  • Managing vAPPs with XOA

    11
    0 Votes
    11 Posts
    4k Views
    G
    @olivierlambert +1 For creating vApps GUI in XO Reason: I recently had this configuration: VM1 - Delay 90 Seconds VM2 - Delay 100 Seconds VM3 - Delay 0 Seconds The VM3 instead of starting first, always starts last without fail. One difference I noticed is that VM3 is UEFI vs VM1 & 2 being in BIOS mode. I read elsewhere in the forum that vApps is the only reliable way to have an order. Maybe if we can somehow ensure that delay works, vApps will become less significant ?
  • Ignition and creating a SUSE MicroOS VM

    11
    0 Votes
    11 Posts
    5k Views
    G
    @Bytevenidos That's an interesting way of doing this, I'll have to remember it. I think the Fuel Ignition tool has a vhd output, it also produces both ignition and combustion parts for you. Worked pretty good on one test machine, but I need to go deeper into some of the other choices you can type in.