• Feedback on immutability

    Pinned Backup
    58
    2 Votes
    58 Posts
    30k Views
    P
    @gsszuber Hi, Yes indeed, you need to preserve the root of the bucket from Lifecycle. We just had a customer with a similar issue. Can you help us by giving a small screenshot of the field to filter out the root (or filter in the three folders) please?
  • After Update XO wont start

    Unsolved Xen Orchestra
    6
    1
    1 Votes
    6 Posts
    869 Views
    D
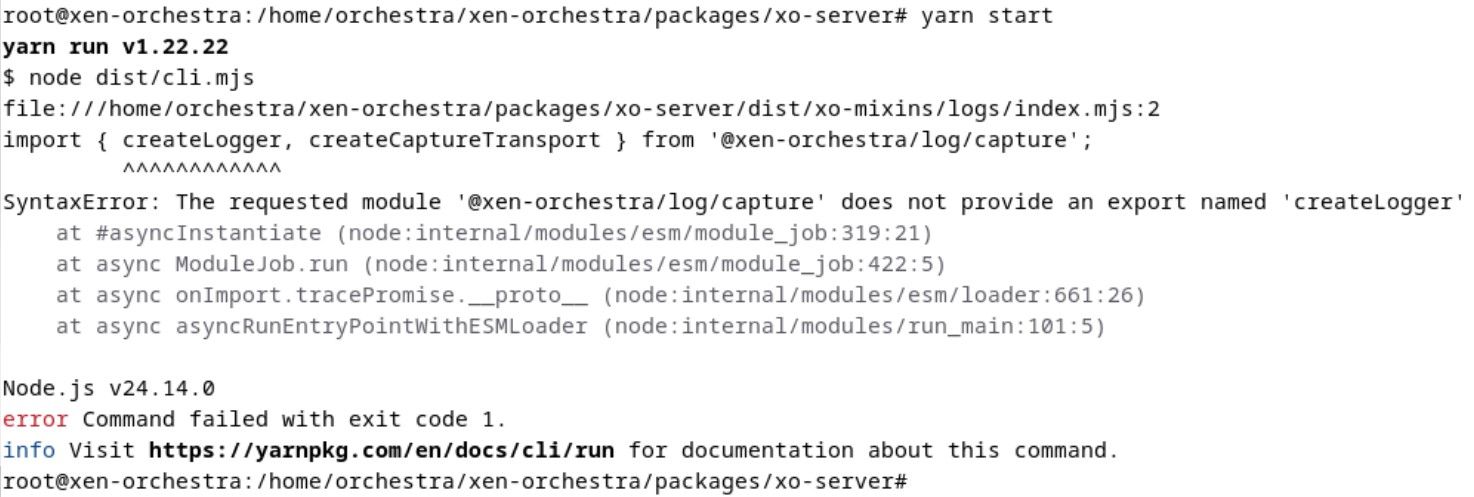
    Hey, that sucks after catching up on 23 commits. Looks like something broke in the log module during the update. I’d try a clean reinstall of the dependencies first, or drop back to an older Node version for a bit since Node 24 can be fussy with these packages. When you need a quick mental break from troubleshooting npm issues, checking out TonyBet is a great way to enjoy some online gaming and sports betting. Hope getting those modules reinstalled gets your build running smoothly again soon!
  • Update Templates

    Xen Orchestra
    14
    1 Votes
    14 Posts
    3k Views
    D
    Hi bikemuch, For unregistered XOA the template auto-update is limited. Easiest way is via CLI: download the latest Debian 13 and CentOS Stream 10 ISOs, then use xe vm-import or create new templates from them. You can also check the XOA “Templates” section and force a refresh if available. Works fine for me this way.
  • Tesla xenctrlext.unix_error Device or resource is busy

    Unsolved Hardware
    13
    2
    0 Votes
    13 Posts
    2k Views
    poddingueP
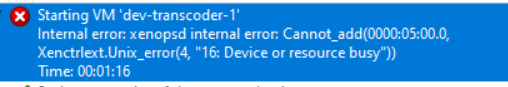
    @seanmcg182 's post might be the answer to the original question, two years late. Your lspci -s 0000:05:00.0 -v at post 8 shows (rev ff) and !!! Unknown header type 7f, which is the same pair he had, and in his case it came from bifurcating the wrong PCIe port in the BIOS rather than from anything XCP-ng was doing. He says the unknown header is what then produced the device or resource busy error on VM start, which is the error you opened with. I don't know whether your board exposes bifurcation the way his X10DRH-CT does, so it might not transfer at all. @kuznetcoff777 if that machine is still around, it'd be worth a look either way.
  • Smart Reboot blocked in XO, and no Rolling Pool Update

    Unsolved XCP-ng
    9
    0 Votes
    9 Posts
    550 Views
    D
    @poddingue said: What I can't tell you is what set that particular combination on your VM in the first place. Does it ring a bell? I have no Idea. I had it on "Protect from accidental shutdown" but turned that off again, later. Doing this again (on, off) helped, as you said. Thank you so much!
  • VM autostart stopped working

    Unsolved XCP-ng
    8
    0 Votes
    8 Posts
    673 Views
    O
    @poddingue Thank you for the analysis. I'd give you a rep if I could
  • Test results for Dell Poweredge R770 with NVMe drives

    Hardware
    37
    7
    0 Votes
    37 Posts
    13k Views
    yannY
    @yllar said: @yannsionneau Hi, any news on the new iso? Hello @yllar In case you missed it, the ISO was released a few days ago: https://xcp-ng.org/blog/2026/08/14/xcp-ng-8-3-lts-refreshed-installation-isos/
  • 0 Votes
    2 Posts
    178 Views
    S
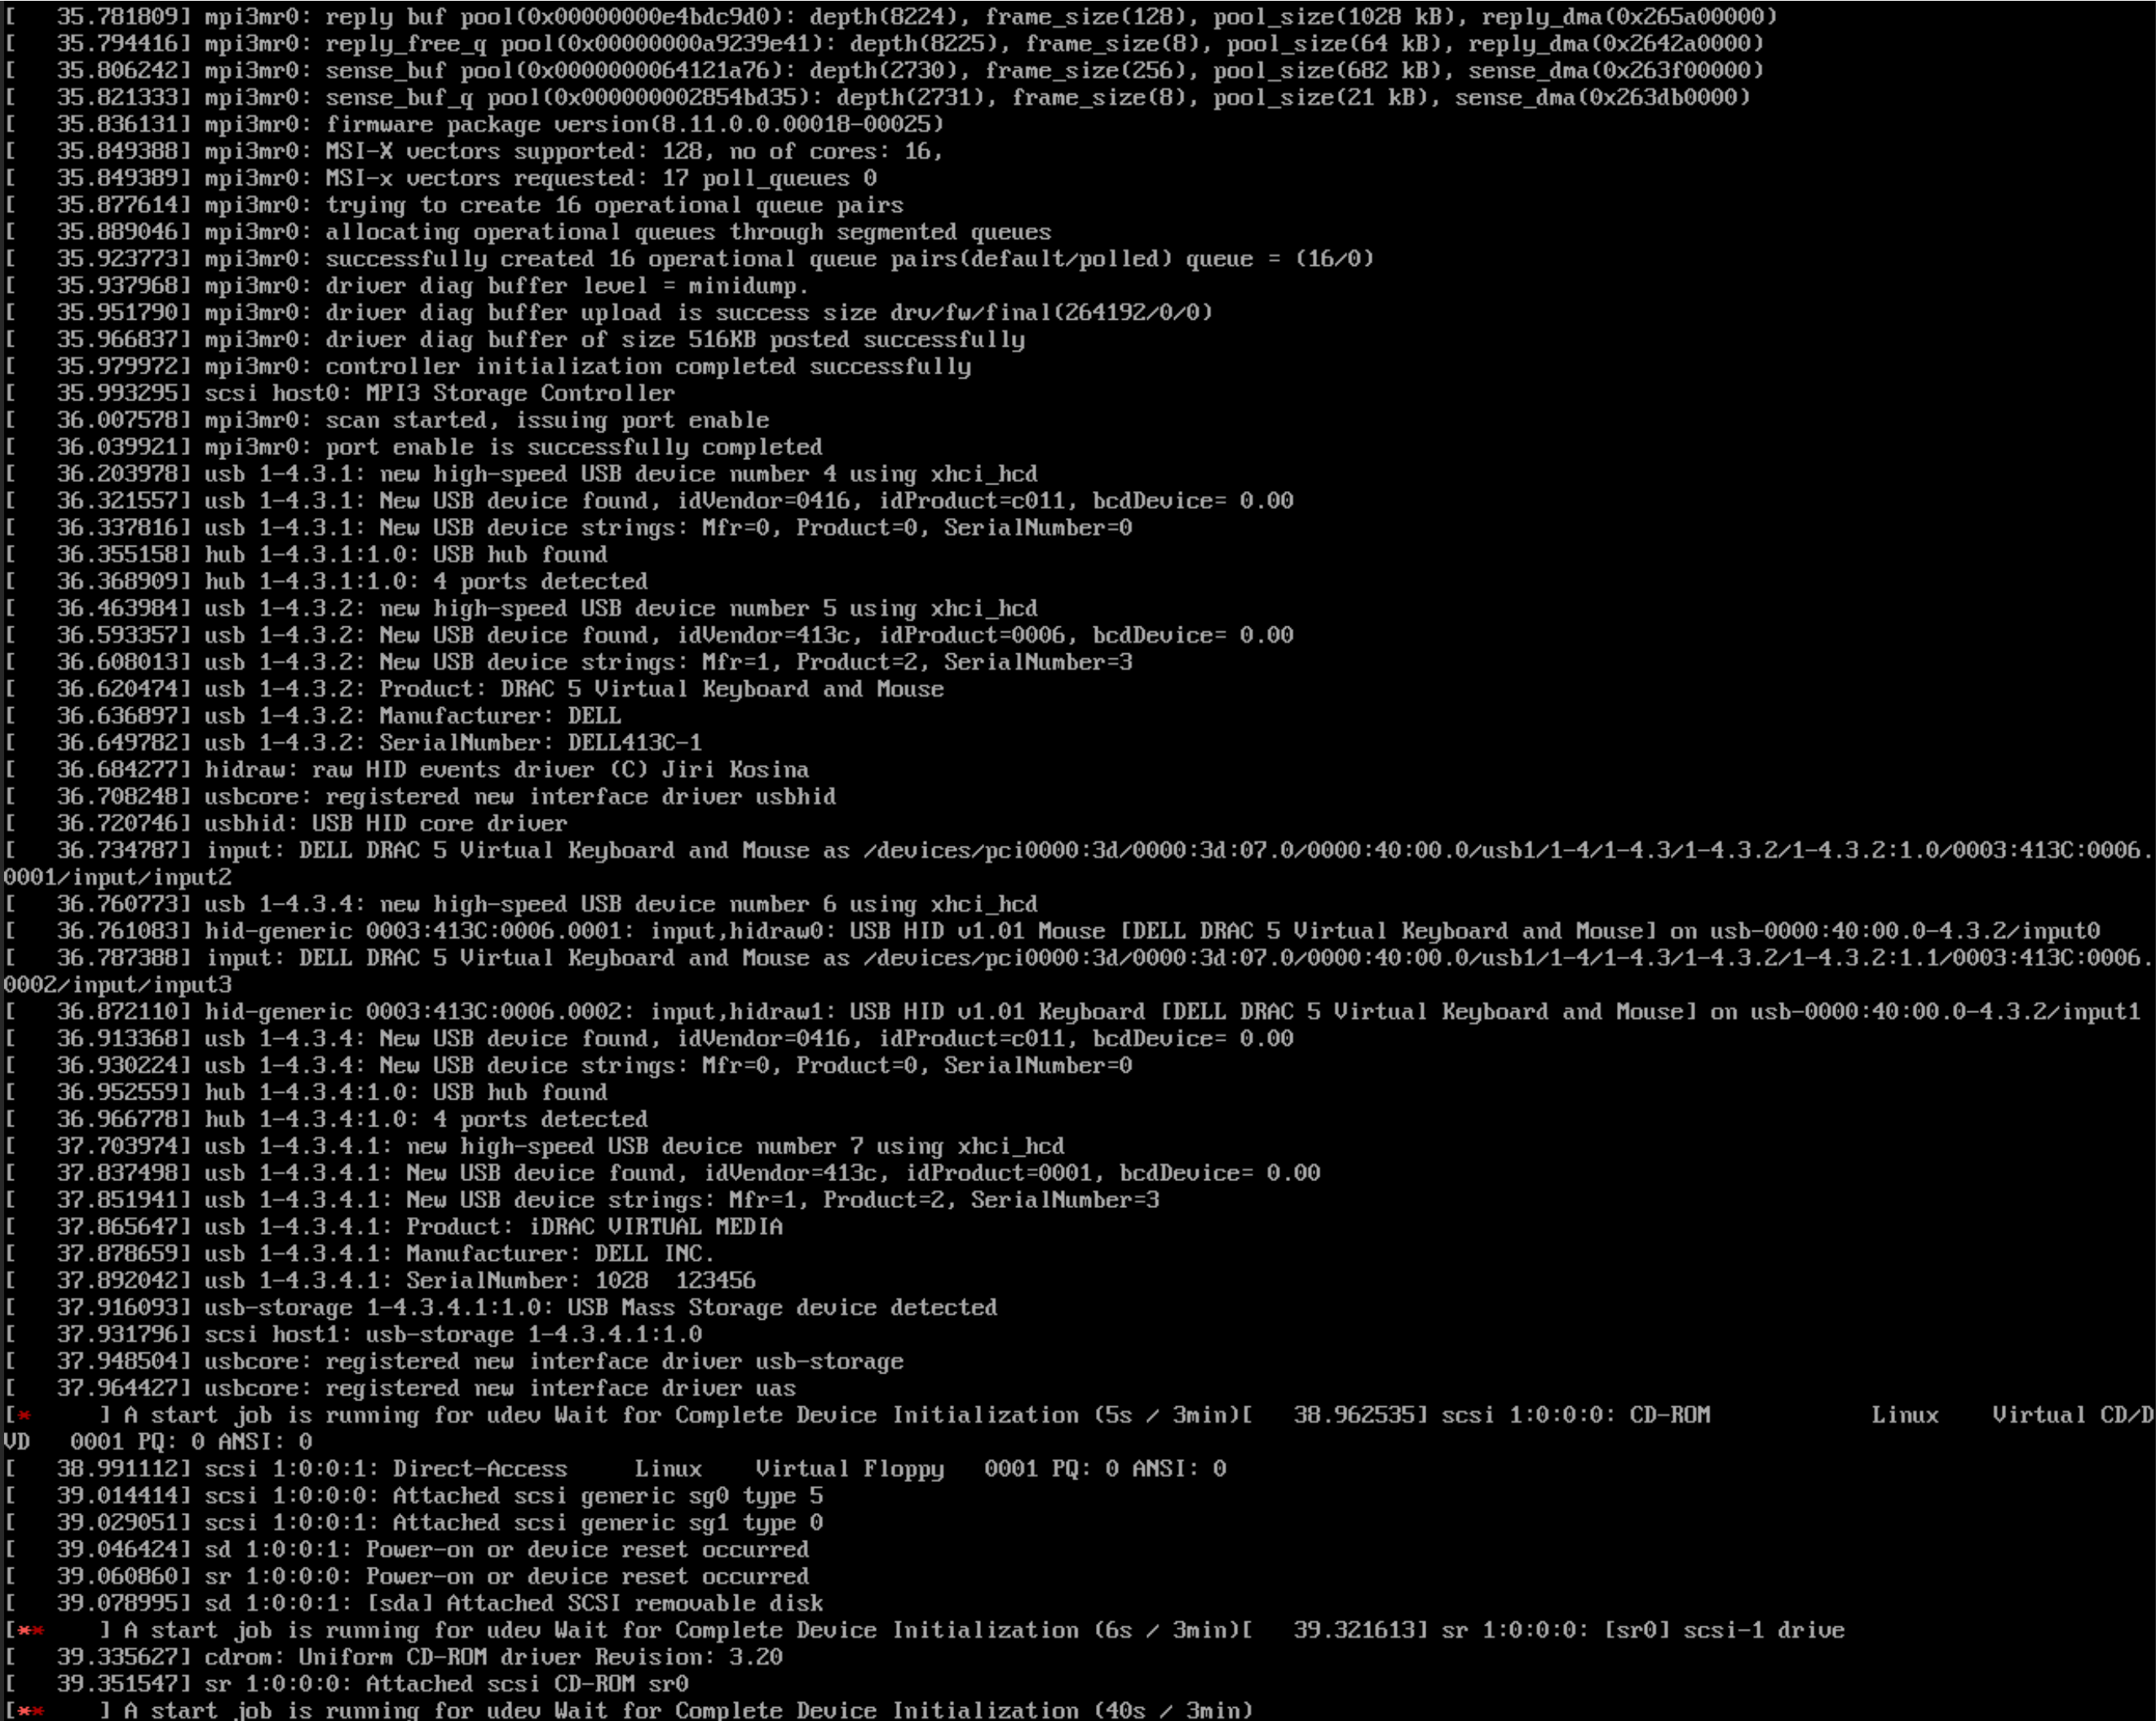
    After a good sleep, I resolved half of my issue. I got my LSI Cards messed up, I accidentally hidan internal LSI3108 (Address 01:00.0) instead of the PCI Card LSI3008 (Address 05:00.0)... My Boot Drives run off of the internal card. From the fallback kernel, I was able to Modify /etc/grub-efi.cfg to remove the internal card form the hidden list. I now have a separate issue, but will make another post.
  • Rolling pool update failed to migrate VMs back

    Unsolved Xen Orchestra
    17
    0 Votes
    17 Posts
    4k Views
    olivierlambertO
    @neal https://github.com/vatesfr/xen-orchestra/issues/10260
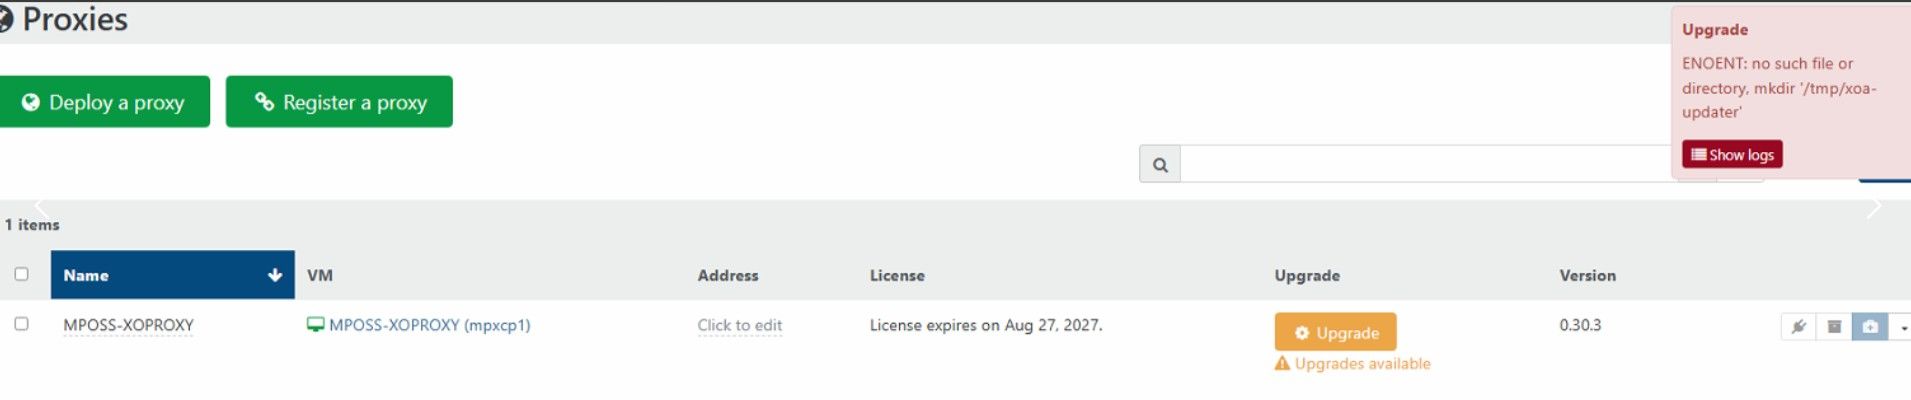
  • is Xo Proxy available in community version

    Unsolved Xen Orchestra
    13
    0 Votes
    13 Posts
    3k Views
    B
    @poddingue Fistst of all I appreciate your answer and your position. The thing is that, even though the proxy code itself is opensource, the functionality of the plugin is basicaly behind a paywall. We are not talking about support. Actual functioning of the plugin after compiling from sources depends on license availability and there is no option to select no support or something along the lines "I built it myself from sources". Without patching the code even though the proxy is otherwise functional the backups won't work because of missing license. Hopefully the powers that can will provide an acceptable albeit community supported way to use the proxy cleanly, without touching license checks. Best regards!
  • Autostart behaviour after upgrade 8.2 -> 8.3

    Solved XCP-ng
    6
    1
    0 Votes
    6 Posts
    448 Views
    poddingueP
    I put both of your questions on a spare host, because I couldn't answer either from memory. On colons: xe creates a key literally called auto_poweron:true with an empty value, so the entries you saw were three separate keys and none was the real auto_poweron, and typing false afterwards just made another one. It exits 0 and prints nothing every time, which I'd call a rough edge rather than a feature, though other-config is free-form by design so I don't know that the CLI is meant to validate keys at all. On the sleep: with rc.local executable and no sleep, it fired at 16 seconds of uptime and xe appliance-start came back with Error: Connection refused (calling connect ), exit 1, in under a tenth of a second. The VM stayed halted and nothing was reported anywhere, since rc.local has no terminal to print to. rc-local.service only orders after basic.target and network.target, nothing toolstack-related, while xapi-wait-init-complete.service took 30 seconds on that host, which is presumably why 60 was barely enough for you. There's an xapi-init-complete.target that looks like the right thing to order a unit against instead of guessing at a delay, though I haven't tried it so treat that as a lead rather than advice. The executable-bit half is in the docs now, it went onto the troubleshooting page after you reported it: https://docs.xcp-ng.org/troubleshooting/common-problems
  • Bad Performance CPU? get-cpufreq-para failed

    Unsolved Compute
    21
    0 Votes
    21 Posts
    5k Views
    poddingueP
    On a Lenovo SR630 V4 it took Power/Performance Bias set to OS Controlled, and on an HPE DL380 Gen 11 it was the iLO Power Regulator moved off Dynamic Power Savings to OS Control Mode, with a host reboot. Both then returned real values from xenpm get-cpufreq-para instead of the failure line. @bleader is right that two vendors is not enough to document, so if your host works, could you post the vendor, the exact setting name, where it lives, and whether you needed a reboot? Dell, Supermicro and anything AMD are the obvious gaps. I don't know whether the firmware is withholding p-state control outright or just not publishing the ACPI objects Xen looks for, so I would rather collect settings than write up a mechanism I can't back. Thanks!
  • v6 UI VDI's not being shown all the time.

    Solved Xen Orchestra
    6
    3
    0 Votes
    6 Posts
    605 Views
    poddingueP
    @acebmxer No problem, that's excellent news, thanks for the feedback!
  • 1 Votes
    7 Posts
    703 Views
    poddingueP
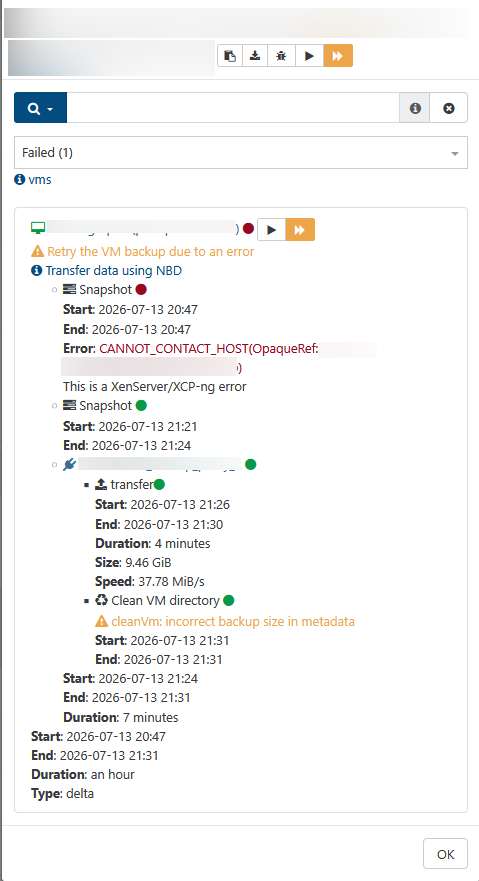
    XO 6.7.0 went out on 30 July, and the changelog carries Bastien's fix under Backups as "Fix failed status on successful retry", pointing at PR https://github.com/vatesfr/xen-orchestra/pull/10129 and back at this thread: https://xen-orchestra.com/blog/xen-orchestra-6-7/. Given what you said about keeping the backup XOA on a version you trust, I would not rush it, but that is the version to look for when you do move. I have not exercised the retry path myself, so if a retried VM still reports the job as failed after you upgrade, it is worth saying so here.
  • CBT: the thread to centralize your feedback

    Pinned Backup
    456
    1 Votes
    456 Posts
    862k Views
    G
    Hello, Just a feedback. I am having trouble using CBT Backups with NBD. Host Details: XCP-NG Version : 8.3 latest (stable) Xen Orchestra: latest:stable (From Source) The first full backup always seems to work. The delta backup gives the error: 'HANDLE_INVALID' the writer IncrementalXapiWriter has failed the step writer.checkBaseVdis() with error HANDLE_INVALID(VBD, OpaqueRef:xxxxx). It won't be used anymore in this job execution. Start: 2026-08-09 14:01 End: 2026-08-09 14:01 Duration: a few seconds Error: HANDLE_INVALID(VBD, OpaqueRef:xxxxxx) This is a XenServer/XCP-ng error
  • 0 Votes
    3 Posts
    209 Views
    olivierlambertO
    No problem, this is always good to have feedback and cases showing an error and the explanation
  • Existing AD Users Cannot Login to XOCE but New Users Can

    Solved Xen Orchestra
    19
    0 Votes
    19 Posts
    4k Views
    K
    RESOLVED — root cause found, three years later. Leaving a full write-up for anyone who lands here from a search. Short version: this was never an XO bug, and it was never intermittent. The answer was sitting in the very first test-cli.js output I posted back in May 2023, and I misread it — as did everyone else in this thread, myself very much included. The line that mattered failed to bind as CN=Agbasi\, Kismet,...: 80090308: LdapErr: DSID-0C090434, comment: AcceptSecurityContext error, data 569, v4f7c We all pattern-matched AcceptSecurityContext error to "bad credentials" and moved on. But the meaning is entirely carried by the data field, which is the underlying Win32 status in hex: data 52e = 0x52E = 1326 = ERROR_LOGON_FAILURE — this is the "wrong password" one data 525 = 1317 = ERROR_NO_SUCH_USER data 532 = 1330 = password expired data 775 = 1909 = account locked out data 569 = 0x569 = 1385 = ERROR_LOGON_TYPE_NOT_GRANTED I was getting 569, not 52e. My password was correct all along. AD validated it, then refused the logon type. Why that happens xo-server-auth-ldap verifies a password the only way LDAP allows — it re-binds to the directory as the user. Against Active Directory, an LDAP simple bind to a DC is processed as a Type 3 (network) logon on that DC. So if an account is caught by "Deny access to this computer from the network" (SeDenyNetworkLogonRight) in the Default Domain Controllers Policy (or any other WINNING GPO, for that matter), it cannot complete an LDAP bind — no matter how correct the password is, and no matter which LDAP client is asking. My environment uses a tiered admin model. Non-domain-admin admin groups are explicitly denied network logon to the DCs. My admin account is in those groups. Hence 569, every single time, by design. Why it looked intermittent It wasn't. I sampled it either side of a config change. I could prove a bind had succeeded recently, because my LDAP-only XO account (no local password on the record at all) minted an API token on 28 July. Then on 31 July I restored RBAC settings on the Default Domain Controllers Policy that had drifted at some point — I found that during unrelated PKI work. GptTmpl.inf last-write confirms it. The token's last successful use is about eleven hours before that edit. Two deterministic states, one config change in the middle. That's the whole "intermittency." My 2023 "seven security groups" theory was wrong For the record, since it's still up there and someone will find it: I removed group memberships one at a time until auth worked, and concluded there was a membership count limit. There isn't. My own control test disproved it at the time — adding fifteen groups never reproduced the failure — and I should have taken that seriously instead of filing it under "weird." The variable was never the count. It was which group. One of the removals happened to drop the account out of a denied group. My other closing theory in this thread — special-character handling in the username or password — was also wrong. Getting 569 back proves AD parsed the escaped DN (CN=Agbasi\, Kismet), found the object, and got as far as evaluating the password. A mangled DN gives you 525 or a DN syntax error, not a logon-rights rejection. ldapts and passport were behaving correctly throughout. How to check this in 60 seconds Run the plugin test CLI and note the data value. Convert hex → decimal, look it up in Microsoft's System Error Codes list. On the DC, look for Security event 4625 with Sub Status 0xC000015B (STATUS_LOGON_TYPE_NOT_GRANTED). Fastest test of all — from a workstation, as the affected account: net use \\dc01\sysvol. If network logon to the DC is denied, this fails too, and you've confirmed it without touching XO at all. Check the policy directly: $p = "\\mydomain.net\SYSVOL\mydomain.net\Policies\{6AC1786C-016F-11D2-945F-00C04fB984F9}" + "\Machine\Microsoft\Windows NT\SecEdit\GptTmpl.inf" Select-String -Path $p -Pattern "SeDenyNetworkLogonRight|SeNetworkLogonRight" Resolve the SIDs and see whether your user is in any of the denied groups. Also worth checking your grant side: if Access this computer from the network doesn't list Authenticated Users directly, ordinary users are probably getting it transitively via Pre-Windows 2000 Compatible Access. Worth confirming before you assume a plain non-privileged account will work. What I am NOT doing Removing those groups from the deny right. It's doing exactly what I rebuilt it to do. Restoring an app login by handing admin groups network access to the DCs for SMB/RPC/LDAP is a bad trade, and I'd just be undoing my own remediation. Fix Interim: local XO accounts for the admins who need them. No AD objects created, nothing to unwind later, per-user attribution preserved in the audit log. Long term: federate XO through Keycloak (OIDC) instead of LDAP. Kerberos ticket issuance is a KDC service operation and is not gated by SeNetworkLogonRight — which is exactly why these accounts log into workstations all day while failing an LDAP bind. ️ Important if you go the Keycloak route: Keycloak's LDAP user federation validates passwords by doing an LDAP bind. Configure it that way and you'll hit data 569 inside Keycloak instead of inside XO and gain nothing. Password validation has to be delegated to Kerberos/GSSAPI. This will bite you on anything else you point at LDAP too — Bitwarden, NPM, TrueNAS, the lot. Worth solving once at the IdP. One request for Vates @olivierlambert @julien-f — you were right that it was environmental, and I owe you both thanks for the time you put in back in 2023. That said, there's a real (small) improvement available here. xo-server collapses every auth provider exception into a generic invalid credentials, and the plugin only emits the actual AD error at DEBUG. The DC told us precisely what was wrong on the very first attempt — it just never reached anywhere a user would look. Surfacing the LDAP result code and the AD data sub-code at INFO on failure, and in the plugin test output in the UI, would turn this class of problem from a multi-year hunt into a single-session diagnosis. Happy to open an issue on GitHub with the full reproduction if that's useful. Hope this saves someone else three years. If you found this thread by searching data 569, *ERROR_LOGON_TYPE_NOT_GRANTED**, or "LDAP invalid credentials but password is correct" — check your Deny access to this computer from the network user right first. That's almost certainly it.
  • 0 Votes
    5 Posts
    319 Views
    M
    Hard reboot sorted itself out
  • XOA Updater fails

    Unsolved Xen Orchestra
    4
    0 Votes
    4 Posts
    689 Views
    andibingA
    @john.c said: nd need to be cleared, before re-attempting the update. Checking the logs will help Just for completeness... it kept doing this after all the typical diagnosis steps. So never found a solution Definitely wasn't cache or disc space related. In the end I built the XOA from source on the same VM and that worked fine. Although subsequent to that I've moved XOA to the containerised version thus saving an extra VM!.
  • Facing some issue in copy Function of Xen Orchestra

    Xen Orchestra
    4
    0 Votes
    4 Posts
    281 Views
    AtaxyaNetworkA
    @irtaza9 i would look a the usual suspect, /var/log/SMlog /var/log/xensource.log see https://docs.xcp-ng.org/troubleshooting/